 PluginStats
NPMScan listing history
By SHYNGYS SHYNBOLATOV · ChatGPT Plugins · Developer Tools
npm package & vuln lookups
ChatGPT Plugins does not publish install or usage counts, so PluginStats tracks NPMScan's listing placement instead, currently position #1239 in the marketplace's popularity-sorted listing.
Category positions: #134 in Developer Tools
About NPMScan
Look up npm package metadata, known vulnerabilities, and CVE details directly from a conversation. NPMScan's MCP server gives AI agents read-only tools backed by the npm registry, OSV.dev, GitHub Security Advisories, GitHub's own API, and the NIST National Vulnerability Database: search packages by name or keyword with download counts, dependent-package counts, and typosquat detection on every result; inspect a package's install scripts, maintainers, license, GitHub stars, and download trend before installing, or compare 2-5 candidates side-by-side with a deterministic pick; check an exact version pinned in a lockfile, or simulate upgrading one before running npm install to see if it's a safe patch or a likely-breaking major bump; query vulnerabilities for one package or up to 100 at once, each finding enriched with severity, a summary, CVE aliases, and the fixed version rather than a bare advisory ID; audit an entire GitHub repository's dependencies (including monorepo workspaces) in one call, or generate a spec-valid CycloneDX/SPDX SBOM with vulnerability and license data embedded; rank the findings from a raw npm audit --json report by CISA KEV/FIRST EPSS exploitation data to know what to fix first, then pull the concrete, ordered remediation playbook for a flagged finding; check an npm maintainer account's publish history for a compromised-account-style cluster, or pull their basic profile; browse the latest npm advisories from either GitHub's curated, mostly CVE-backed reviewed set or its known-malicious-package malware feed, filterable by severity, vulnerability category (XSS, SQL/NoSQL Injection, SSRF, Access Control, Code Injection, and 15 more, reviewed only), affected package, or an exact GHSA/CVE ID; and look up authoritative CVSS/CWE data for any CVE across any ecosystem, enriched with CISA's Known Exploited Vulnerabilities status and FIRST.org's EPSS exploitation-probability score. No API key or authentication is required, and every result links back to the full write-up on npmscan.com.
Description from the ChatGPT Plugins listing.
README badge
Show your rank in a README or on your website. The badge updates automatically.
Charts
Images: 30d · 1y · all time · 1600×900 dark
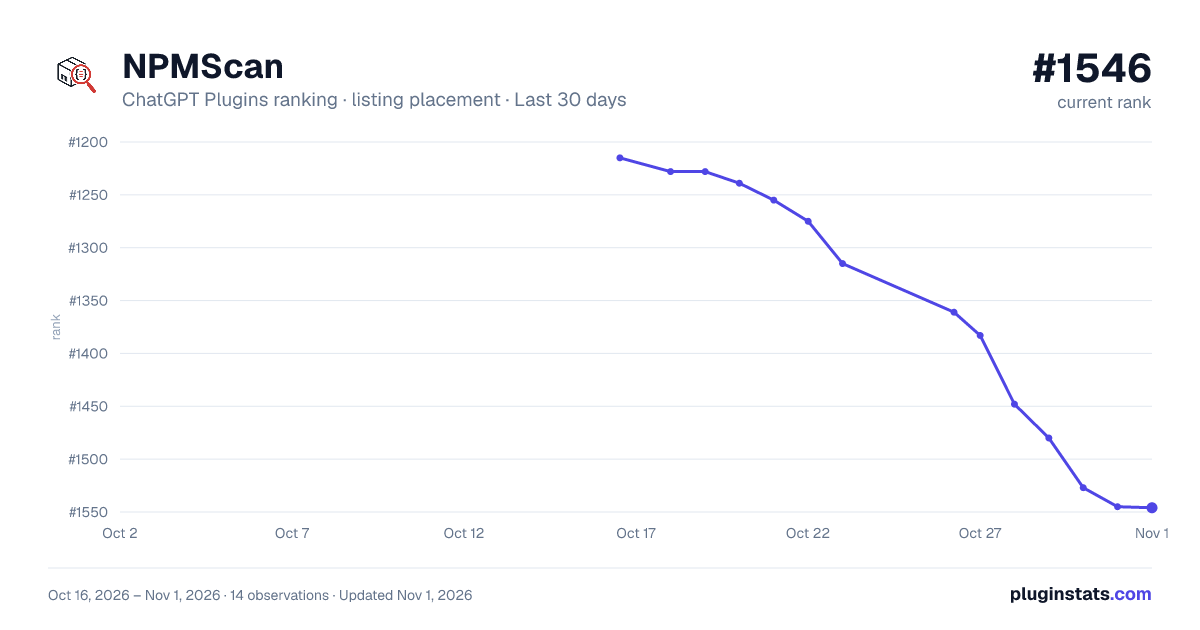
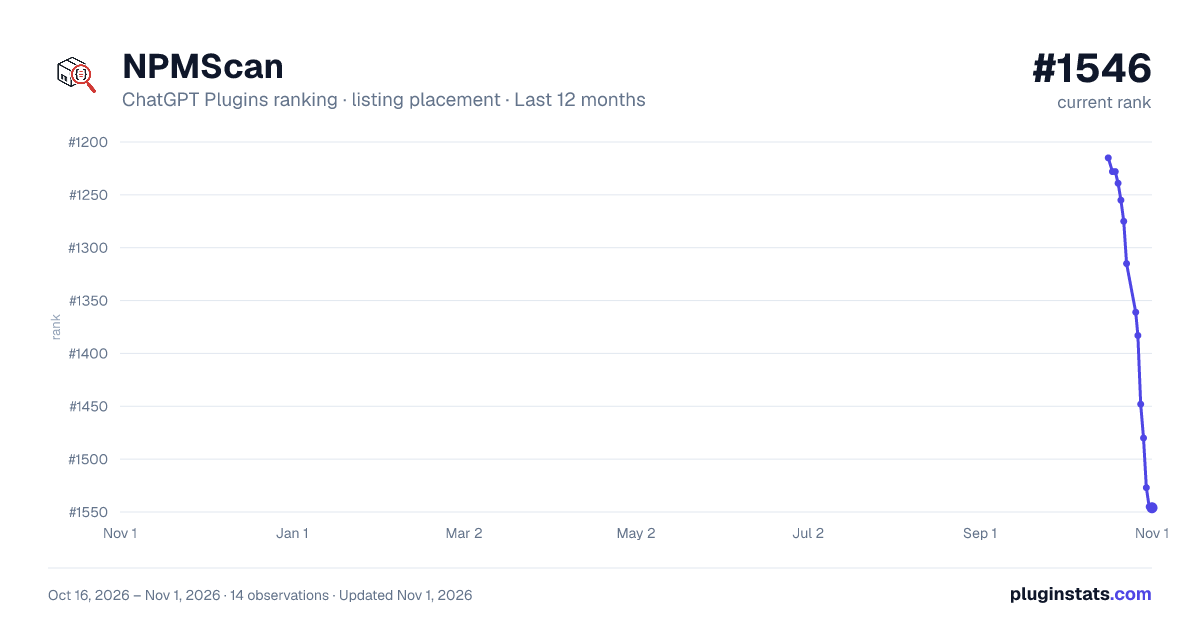
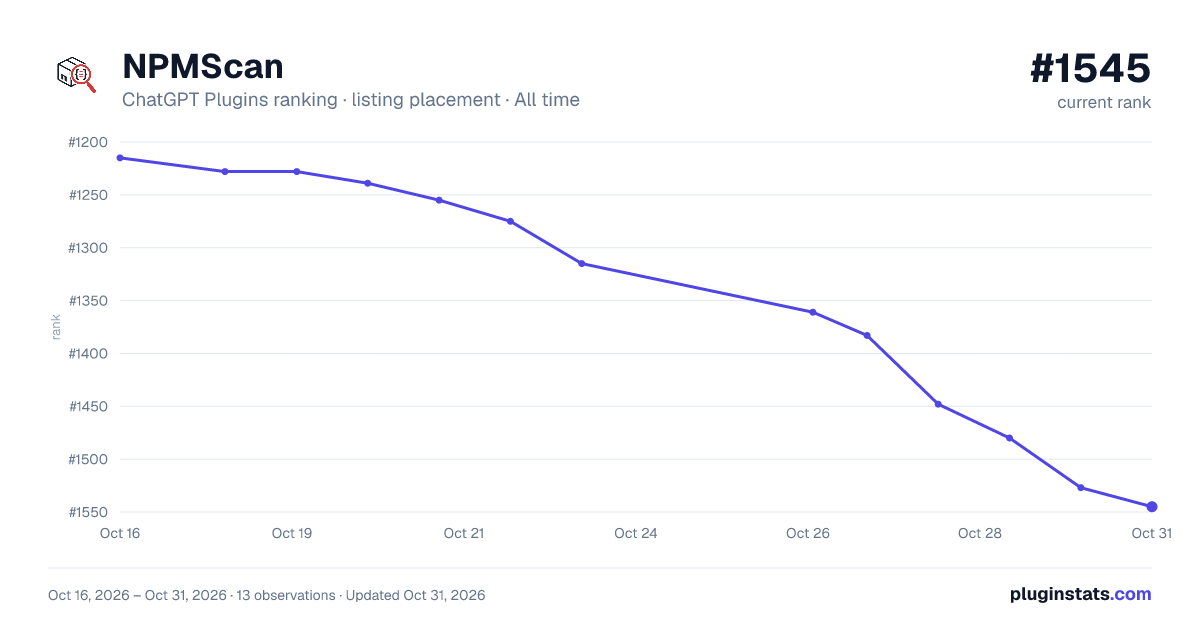

Ranking history
Filled points are observed values; hollow points come from Internet Archive snapshots of the listing page. Dashed segments span periods with no observations — values between points are not interpolated.
Similar ChatGPT Plugins Developer Tools plugins
All 20 NPMScan alternativesData source
OpenAI does not publish install counts or ratings for ChatGPT plugins. PluginStats records listing details and each plugin's placement in the directory over time: overall position follows the Popular list, then New & Noteworthy, then each category in directory order.
Listing: https://chatgpt.com/plugins/plugin_asdk_app_6a6a699e6f3481918d5e6034432894f2. First seen Oct 16, 2026; last successful collection Oct 20, 2026. See the methodology.