 PluginStats
QWED Security installs statistics
By QWED · GitHub Marketplace
Deterministic security verification for PRs and releases. Emits proof-bound verdicts and blocks unsafe code merge
QWED Security has 5 recorded installs on GitHub Marketplace.
It ranks #1133 of 1,393 tracked GitHub Marketplace listings by installs.
PluginStats has 1 daily observations since Oct 16, 2026; the latest is from Oct 16, 2026.
About QWED Security
Deterministic security verification for PRs and release boundaries. Evidence → Context → Policy pipeline emits a Verification Context v1.0 document with proof-bound verdicts. Merge gates open only on ADMIT. Full-codebase visibility, PR-scoped gating — blocks only what the PR introduces, not existing debt. No LLM, no heuristics, fail-closed.
Capabilities
• Verification Context v1.0 — Every scan emits a machine-readable document with verdict (VERIFIED / UNVERIFIABLE / BLOCKED), admission (ADMIT / DENY), and a SHA-256 proof reference binding evidence to the decision.
• Merge Gating — Check run succeeds only when admission is ADMIT. UNVERIFIABLE and BLOCKED fail closed.
• Context-Aware Classification — Distinguishes runtime code, tests, docs, literal strings, and config before deciding.
• Deterministic Policy Engine — Evidence → Context → Policy pipeline. No AI scoring, no probabilistic pass logic.
• AST + Pattern Analysis — Detects dangerous execution primitives, unsafe constructs, and security-sensitive patterns.
• ReleaseBoundaryGuard — Verifies what ships in Python, npm, and Docker artifacts. Blocks secret leakage in release surfaces.
• Secret Detection — Flags credentials, tokens, and high-risk data exposure across code and config.
• VC in PR Comments — Full Verification Context published as a collapsible PR comment for audit.
Benefits
• Reduced False Positives — Separates executable risk from inert code (tests, docs, literals). • Fail-Closed — Unknown states never pass silently. • Machine-Readable Evidence — Schema-validated VC contract for downstream tooling. • Explainable — Every finding includes context classification and policy reasoning. • Release Surface Coverage — Enforces security on what actually ships.
Getting Started
• Install the GitHub App • Select repositories • QWED scans pull requests automatically • Review in GitHub Checks: • VERIFIED (ADMIT) → merge allowed • UNVERIFIABLE (DENY) → review required • BLOCKED (DENY) → must fix
Use Cases
• Gate merges on deterministic verification • Block unsafe execution patterns • Detect secrets before they land • Enforce release boundaries for packages/containers • Feed VC documents into compliance pipelines
Description from the GitHub Marketplace listing.
- Security
- Code quality
Where QWED Security sits in the listing
Each band is one page of 20. Installs on a log scale. Placement is projected from installs, so it can differ from the marketplace's own sort order. Hover a dot to see the listing.


Charts
Images: 30d · 1y · all time · 1600×900 dark
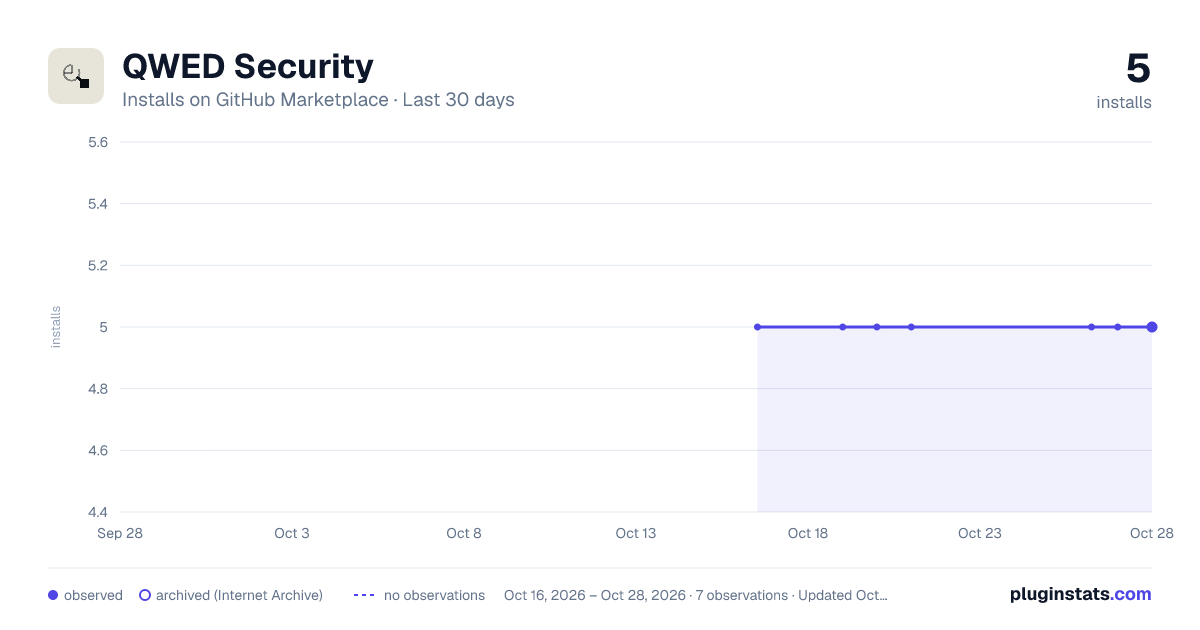
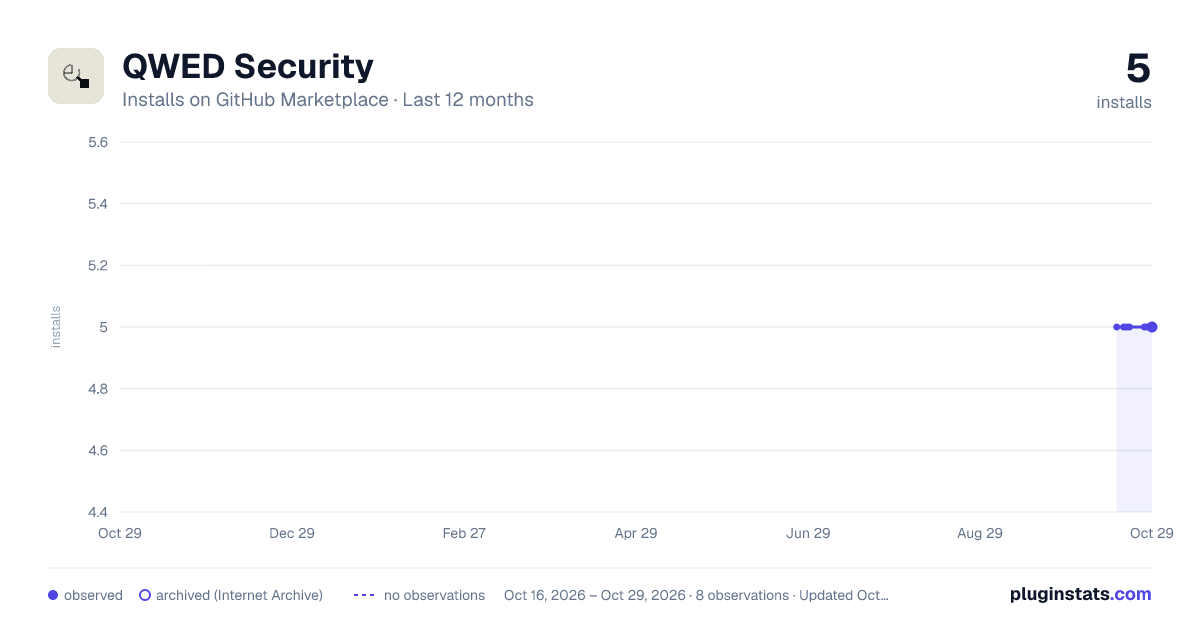
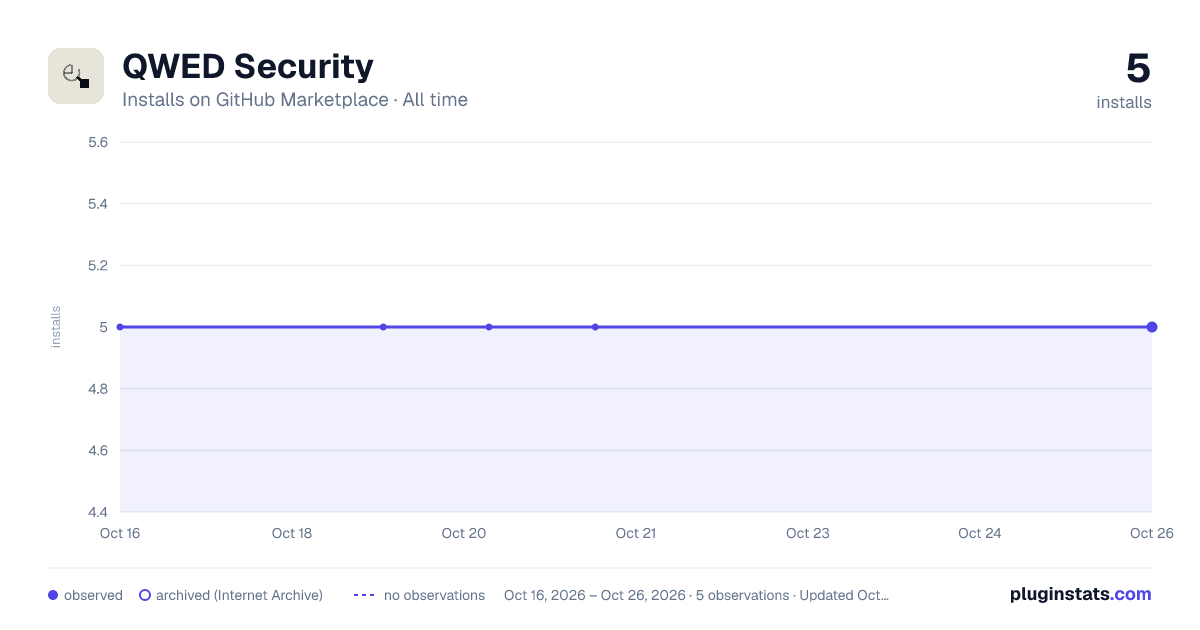

Adoption over time


7/30/90-day growth


Filled points are observed values; hollow points come from Internet Archive snapshots of the listing page. Dashed segments span periods with no observations — values between points are not interpolated.
Recent observations
Full history (1)Similar GitHub Marketplace plugins
Data source
Install counts (installations of each GitHub App across accounts and organizations) are read from public GitHub Marketplace listing pages. GitHub does not publish ratings. Category positions reflect GitHub's own popularity sort.
Listing: https://github.com/marketplace/qwed-security. First seen Oct 16, 2026; last successful collection Oct 16, 2026. See the methodology.