 PluginStats
Runenv - inject secrets at runtime installs statistics
By Jambo company · GitHub Marketplace
Stop sharing files. RunEnv injects secrets into memory at runtime
Runenv - inject secrets at runtime has 6 recorded installs on GitHub Marketplace.
It ranks #1118 of 1,393 tracked GitHub Marketplace listings by installs.
PluginStats has 1 daily observations since Oct 16, 2026; the latest is from Oct 16, 2026.
About Runenv - inject secrets at runtime
RunEnv injects end-to-end encrypted secrets directly into your GitHub Actions at runtime. Stop copy-pasting .env files and securely sync your environment variables across your entire pipeline, from local development to production with zero disk writes.
Capabilities
• Automated Secret Injection: Seamlessly inject E2EE (End-to-End Encrypted) secrets directly into your pipelines at runtime without writing to disk. • Environment Parity Control: Automatically map the correct variables to your development, staging, or production environments. • Unused Secret Detection: Automatically scan and receive warnings for secrets that have gone completely unused for over 30 days to reduce your attack surface. • AST Workflow Validation: Proactively check your GitHub Actions codebase to warn you if your scripts call for an environment variable that hasn't been defined in RunEnv.
Benefits
• Zero-Disk Security: Completely eliminates .env files from your CI/CD runners, preventing secrets from leaking into logs or cache layers. • Streamline CI/CD Pipelines: Fixes "works on my machine" bugs by ensuring your CI/CD pipeline fetches the exact same secrets your developers are using locally, instantly. • Granular Access Control: Uses scoped machine tokens and Strict Role-Based Access Control (RBAC) so pipelines only access the environments they absolutely need.
Getting Started
Requirements:
• Plan: Available on all RunEnv plans (including the Free tier). • User Permissions: You must be an Owner or Admin of the RunEnv project to generate machine tokens.
Setup Process:
• Log into your RunEnv dashboard and navigate to your project. • Go to the Integrations or Settings tab to generate a scoped Machine Token for your desired environment (e.g., production). • Add this token to your GitHub Repository Secrets as RUNENV_MACHINE_TOKEN.
Description from the GitHub Marketplace listing.
- Security
Where Runenv - inject secrets at runtime sits in the listing
Each band is one page of 20. Installs on a log scale. Placement is projected from installs, so it can differ from the marketplace's own sort order. Hover a dot to see the listing.


Charts
Images: 30d · 1y · all time · 1600×900 dark
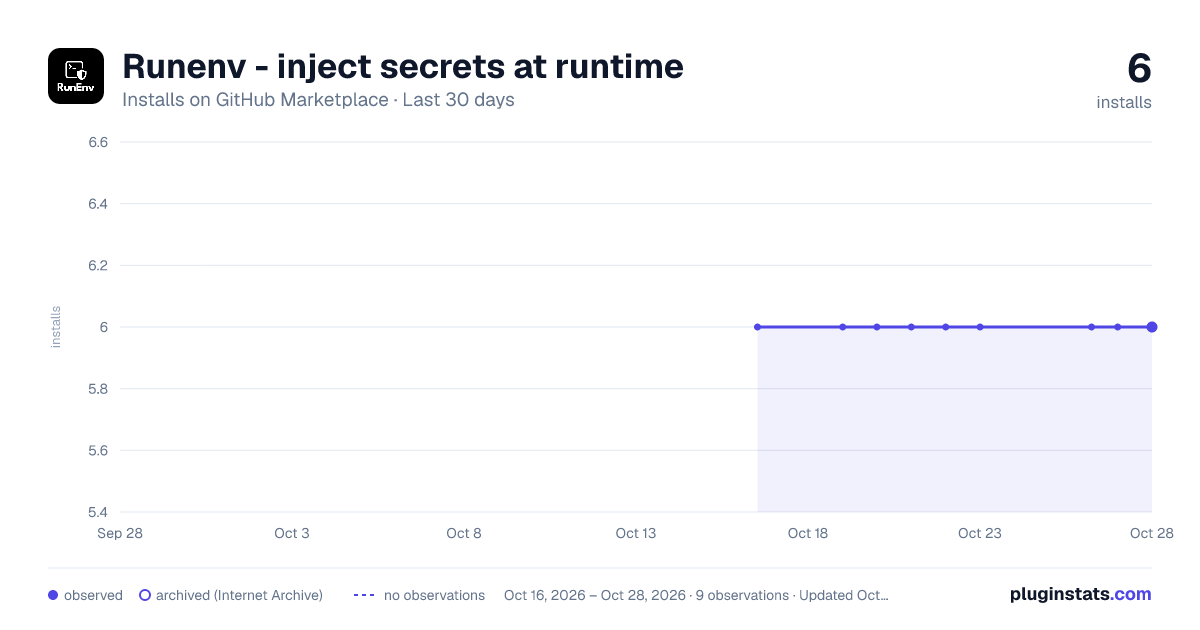

Adoption over time


7/30/90-day growth


Filled points are observed values; hollow points come from Internet Archive snapshots of the listing page. Dashed segments span periods with no observations — values between points are not interpolated.
Recent observations
Full history (1)Similar GitHub Marketplace plugins
Data source
Install counts (installations of each GitHub App across accounts and organizations) are read from public GitHub Marketplace listing pages. GitHub does not publish ratings. Category positions reflect GitHub's own popularity sort.
Listing: https://github.com/marketplace/runenv-inject-secrets-at-runtime. First seen Oct 16, 2026; last successful collection Oct 16, 2026. See the methodology.