 PluginStats
ecc-agentshield weekly downloads statistics
By affaan-m (2 listings) · npm · MCP servers
Security auditor for AI agent configurations. Scans Claude Code setups for vulnerabilities, misconfigs, and injection risks.
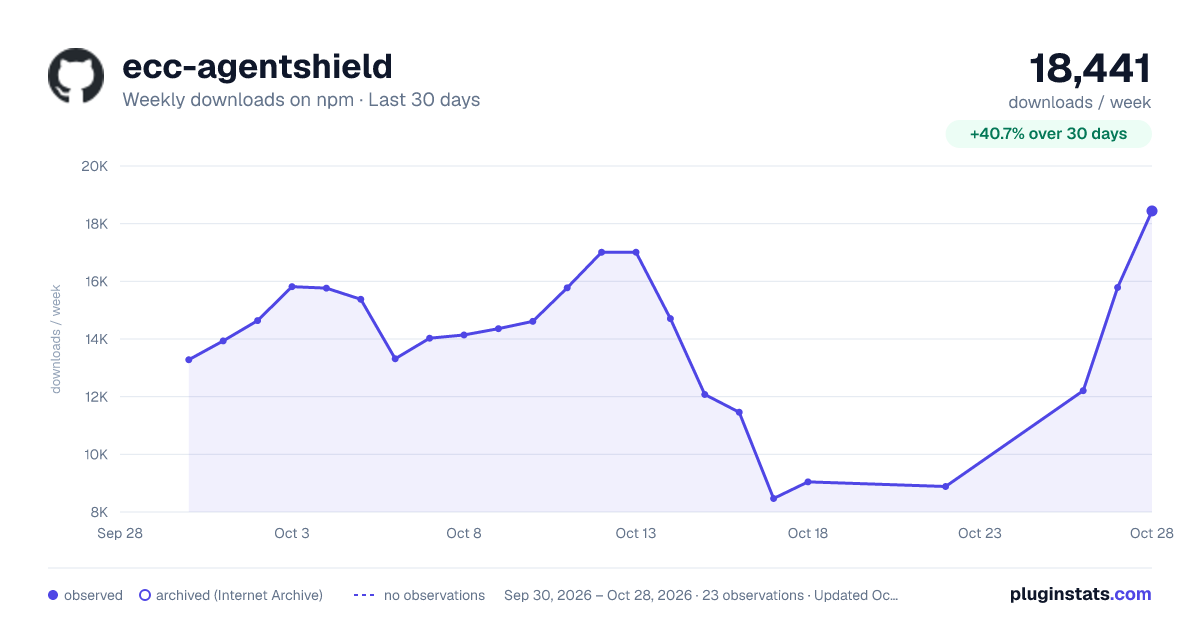
ecc-agentshield has 8,468 recorded weekly downloads on npm, a decrease of 21.5% over the past 30 days.
It ranks #953 of 2,251 tracked npm listings by weekly downloads.
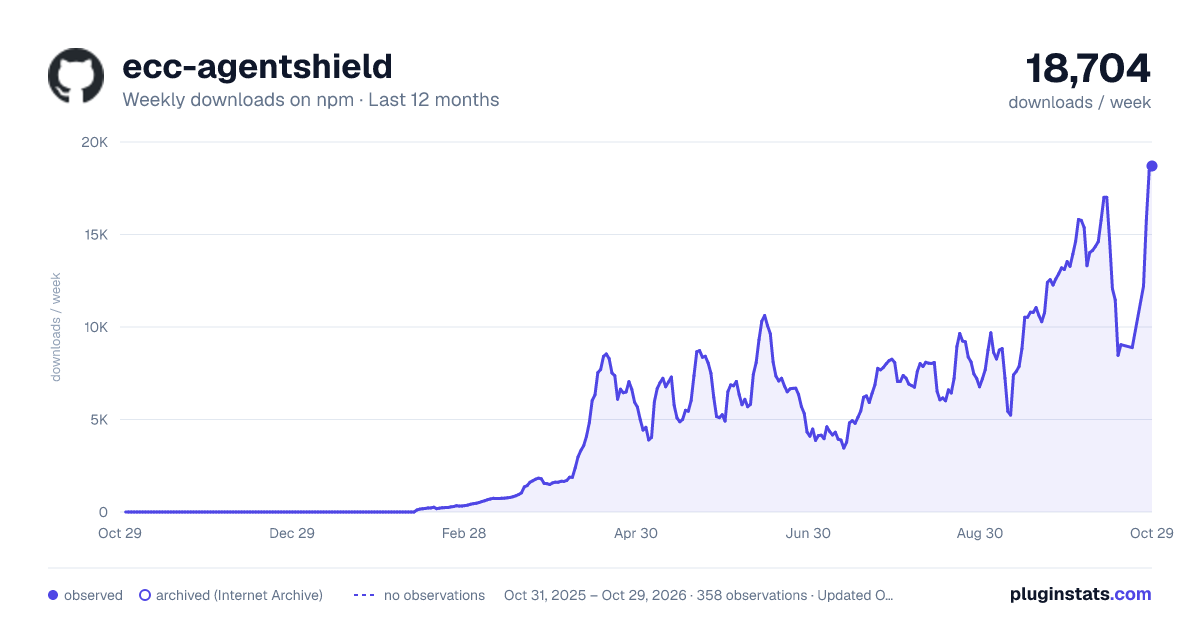
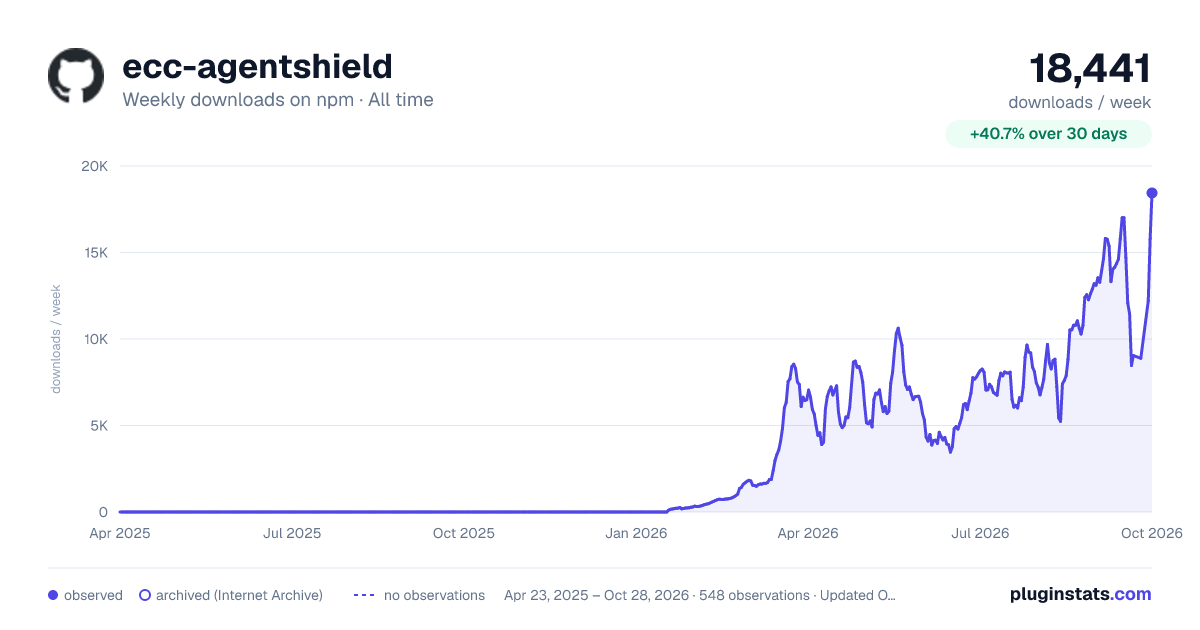
Over 90 days, weekly downloads changed by +36.5%.
PluginStats has 543 daily observations since Apr 23, 2025; the latest is from Oct 17, 2026.
About ecc-agentshield
AgentShield
Security auditor for AI agent configurations
Scans Claude Code setups for hardcoded secrets, permission misconfigs, hook injection, MCP server risks, and agent prompt injection vectors. Available as CLI, GitHub Action, and GitHub App integration.
Quick Start · What It Catches · API Reference · Opus Pipeline · GitHub Action · Distribution · MiniClaw · Changelog
Preferred compute sponsor: Run or self-host any open-source model. Itô is ECC's suggested compute provider. Any GPU provider works. ECC only links to the Itô dashboard for sign-in and GPU rental or management; it does not create or manage rentals or provision compute or serving. Managed inference through Itô is not live yet.
Why
The AI agent ecosystem is growing faster than its security tooling. In January 2026 alone:
• 12% of a major agent skill marketplace was malicious (341 of 2,857 community skills) • A CVSS 8.8 CVE exposed 17,500+ internet-facing instances to one-click RCE • The Moltbook breach compromised 1.5M API tokens across 770,000 agents
Developers install community skills, connect MCP servers, and configure hooks without any automated way to audit the security of their setup. AgentShield scans your .claude/ directory and flags vulnerabilities before they become exploits.
Built at the Claude Code Hackathon (Cerebral Valley x Anthropic, Feb 2026). Part of the Everything Claude Code ecosystem (42K+ stars).
Quick Start
That's it. AgentShield auto-discovers your ~/.claude/ directory, scans all config files, and prints a graded security report.
Discovery intentionally skips common generated directories such as node_modules, build output, and .dmux worktree mirrors so transient copies do not duplicate findings.
More commands
JSON reports now expose findings[].runtimeConfidence when AgentShield can distinguish active runtime config from project-local settings, template/example inventories, installed Claude plugin caches, declarative plugin manifests, and manifest-resolved non-shell hook implementations. Reports also include local harness adapter evidence for Claude Code, OpenCode, Codex, Gemini, Zed, VS Code, dmux, terminal-agent wrappers, and project-local templates when matching markers are present.
What It Catches
268 rules across 15 modules, graded A to F with a 0 to 100 numeric score. Recognized defenses are listed and never penalized.
Scoring and recognized defenses
The score starts at 100 per category and only findings deduct from it: critical 25, high 15, medium 5, low 2, info 0. Protective configuration the scanner finds (deny and ask lists, sandbox settings, blocking PreToolUse hooks, read-only agent tool lists, Codex sandbox_mode, Hermes manual approvals, and similar) is listed in every report under "Recognized Defenses" so it gets credit and is visibly never penalized. Defenses do not add points either: the score cannot be gamed by adding decorative deny rules, it can only be lowered by real findings. Guard-pattern findings the permission rules emit at info severity ("Deny/ask rule blocking ...", "Prohibition of ...", "Mention of ...") are enforced to a zero deduction in src/reporter/score.ts.
Secrets Detection
| What | Examples |
| API keys | Anthropic (sk-ant-), OpenAI (sk-proj-/sk-), xAI (xai-), AWS (AKIA), Google/Gemini (AIza), Stripe (sk_test_/sk_live_) | | Tokens | GitHub PATs (ghp_/github_pat_), Linear (lin_api_), Cloudflare (CF_API_TOKEN=), Slack (xox[bprs]-), JWTs (eyJ...), Bearer tokens | | Credentials | Hardcoded passwords, database connection strings (postgres/mongo/mysql/redis), private key material | | Env leaks | Secrets passed through environment variables in configs, echo $SECRET in hooks |
Permission Audit (17 rules)
| What | Examples |
| Wildcard access | Bash(*), Write(*), Edit(*) — unrestricted tool permissions | | Missing deny lists | No deny rules for rm -rf, sudo, chmod 777 | | Dangerous flags | --dangerously-skip-permissions usage | | Mutable tool exposure | All mutable tools (Write, Edit, Bash) allowed without scoping | | Destructive git | git push --force, git reset --hard in allowed commands | | Unrestricted network | curl *, wget, ssh *, scp * in allow list without scope |
Hook Analysis (40 rules)
| What | Examples |
| Command injection | ${file} interpolation in shell commands — attacker-controlled filenames become code | | Data exfiltration | curl -X POST with variable interpolation sending data to external URLs | | Silent errors | 2>/dev/null, \|\| true — failing security hooks that silently pass | | Missing hooks | No PreToolUse hooks, no Stop hooks for session-end validation | | Network exposure | Unthrottled network requests in hooks, sensitive file access without filtering | | Session startup | SessionStart hooks that download and execute remote scripts | | Package installs | Global npm install -g, pip install, gem install, cargo install in hooks | | Container escape | Docker --privileged, --pid=host, --network=host, root volume mounts | | Credential access | macOS Keychain, GNOME Keyring, /etc/shadow reads | | Reverse shells | /dev/tcp, mkfifo + nc, Python/Perl socket shells | | Clipboard access | pbcopy, xclip, xsel, wl-copy — exfiltration via clipboard | | Log tampering | journalctl --vacuum, rm /var/log, history -c — anti-forensics |
MCP Server Security (49 rules)
| What | Examples |…
Description from the npm listing.
- claude-code
- security
- ai-agent
- mcp
- hackathon
- opus
- anthropic
- scanner
- audit
Where ecc-agentshield sits in the listing
Each band is one page of 20. Weekly downloads on a log scale. Placement is projected from weekly downloads, so it can differ from the marketplace's own sort order. Hover a dot to see the listing.


Charts
Images: 30d · 1y · all time · 1600×900 dark

Adoption over time


7/30/90-day growth


Filled points are observed values; hollow points come from Internet Archive snapshots of the listing page. Dashed segments span periods with no observations — values between points are not interpolated.
Recent observations
Full history (543)Similar npm MCP servers plugins
Data source
Weekly downloads (trailing 7 complete days) come from the official npm downloads API. Downloads include CI and mirrors and are not equivalent to installs or users. npm publishes no ratings.
Listing: https://www.npmjs.com/package/ecc-agentshield. First seen Oct 16, 2026; last successful collection Oct 18, 2026. See the methodology.